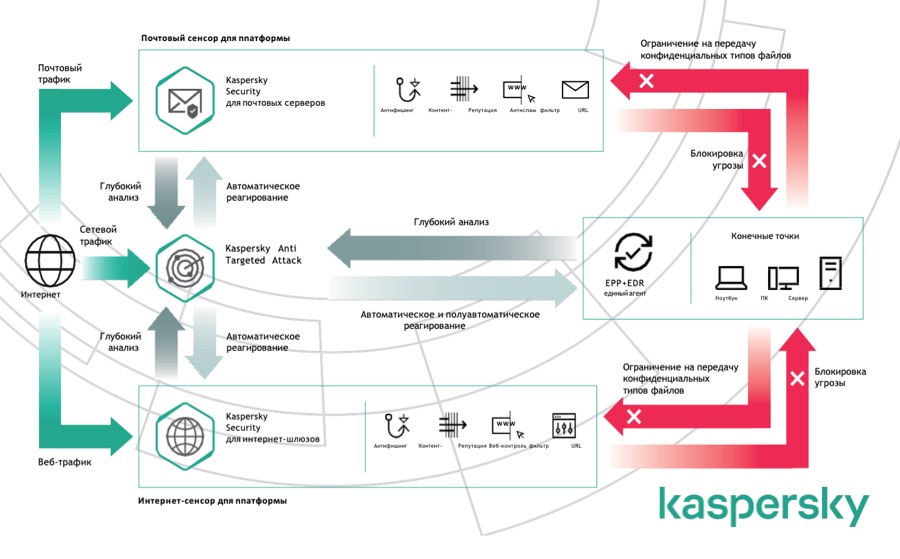
The Kaspersky Anti Targeted Attack platform is an Extended Detection and Response solution that provides comprehensive protection against sophisticated threats and targeted attacks, letting you monitor all entry points of potential threats – the network, web traffic, email, PCs, laptops, servers and virtual machines. In addition to built-in advanced detection and analysis technologies, the platform is enriched with threat intelligence (Threat Intelligence) and maps detections to the MITRE ATT&CK knowledge base of adversary tactics and techniques.
The Kaspersky Anti Targeted Attack platform is fully integrated with Kaspersky Security for Business through a single agent shared with Kaspersky EDR. The platform also integrates with Kaspersky Security for Mail Servers and Kaspersky Security for Internet Gateways, which act as sensors and enable automatic response, at the network level, to more sophisticated threats found by the platform.
The Kaspersky Anti Targeted Attack platform allows you to:
- Implement a single reliable system for protecting corporate infrastructure against sophisticated threats and targeted attacks
- Reduce the workload of the information security team
- Optimize the cost of investigating and responding to complex incidents
- Ensure compliance with regulatory requirements
Key features
- A multi-layered architecture provides absolute visibility through the joint operation of network, email and web sensors as well as endpoint agents.
- Powerful analytics modules work with data from network sensors (network traffic analysis) and endpoint agents (EDR functionality), enabling fast verdicts.
- A high-performance sandbox lets you run suspicious objects in an isolated environment and analyze them at multiple levels. The ability to investigate the behavior of analyzed objects in detail and to map detected suspicious activity to the MITRE ATT&CK knowledge base allows you to respond promptly to complex incidents.
- Retrospective analysis – including when endpoints are unavailable and data is encrypted. This is possible thanks to automated collection of data, objects and verdicts in a centralized repository.
- Threat intelligence working in two modes – automatic checks against the global reputation data of Kaspersky Security Network and access to the Kaspersky Threat Intelligence portal.
- Automatic search for sophisticated threats. Events are matched against a unique set of indicators of attack and the MITRE ATT&CK knowledge base of adversary tactics and techniques, which contains clear descriptions, examples and response recommendations.
- Comprehensive protection of the business against sophisticated attacks. Analysts can compose complex queries to search for anomalous behavior, MITRE ATT&CK techniques, and suspicious activity and threats specific to your infrastructure
Benefits of the Kaspersky Anti Targeted Attack platform
- Reduced information security risks
- Higher productivity and quality of work of IT and information security department staff
- Optimized labor costs
- of highly qualified personnel
- Fewer routine manual operations
- More incidents handled without additional labor costs
- Collection, storage and provision of information on information security incidents within the requirements of internal and external regulation and industry legislation
Compliance with regional and international legislation
The Kaspersky Anti Targeted Attack platform helps organizations comply with banking industry standards, PCI DSS, as well as the regulatory requirements of the State Technical Service of the National Security Committee of the Republic of Kazakhstan.Kaspersky Endpoint Detection and Response
Kaspersky Endpoint Detection and Response (EDR) is a powerful information security system that gives security specialists a complete picture of events across the workstation and server infrastructure and provides effective protection against sophisticated threats and APT attacks.
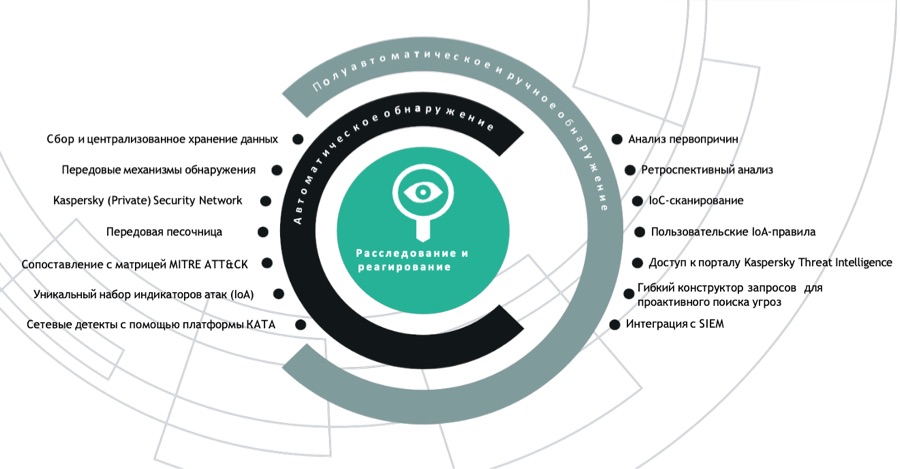
Kaspersky EDR offers reliable endpoint protection and improves the efficiency of your SOC. The solution collects, records and centrally stores information about security events on all endpoints, which provides prompt access to retrospective data when investigating prolonged attacks, even when endpoints are unavailable or data has been encrypted or destroyed by attackers. Advanced investigation features based on unique indicators of attack (IoA), mapping to the MITRE ATT&CK knowledge base of adversary tactics and techniques, a flexible query-building tool and access to the Kaspersky Threat Intelligence portal – all of this enables effective threat detection and rapid incident response, helping to prevent potential damage.
Key benefits:
- Kaspersky EDR complements the endpoint protection platform – Kaspersky Security for Business – by offering powerful detection, investigation and response capabilities that significantly raise the level of security. A single agent for automatic protection against mass threats and advanced protection against sophisticated attacks makes incident management easier and minimizes additional maintenance costs. No additional load on endpoints and no additional expense – just confidence that your endpoints and servers are reliably protected against sophisticated and targeted attacks.
- Kaspersky EDR reduces the time required for the initial collection of digital evidence and telemetry analysis, speeding up incident response from hours to minutes. The solution automates as far as possible the routine tasks of identifying, prioritizing, investigating and neutralizing sophisticated and APT threats. A high degree of automation combined with ease of use increases the engagement of security specialists and reduces the need for additional resources while increasing the overall number of properly handled incidents.
- Kaspersky EDR can be part of the Kaspersky Anti Targeted Attack (KATA) platform, combining EDR capabilities with advanced threat detection at the network level. Security specialists get all the tools they need for multi-angle threat detection at both the endpoint and network levels at the same time. The solution allows you to investigate incidents effectively, hunt for threats proactively and respond to them quickly and centrally.
- Improve the effectiveness of protection with a powerful enterprise solution for incident detection and response
- Strengthen control over the endpoint infrastructure and improve the detection of sophisticated threats using advanced technologies
- Automate threat detection and response without disrupting business operations
- Streamline threat detection, incident management and response processes, allocating resources optimally
- Improve the efficiency of the in-house security operations center (SOC)
Contacts
Sales department and GEPmC project office
info@gepmc.com · 282 Dostyk Ave, office 205, Almaty